


The chief executive officer of Canada’s largest grocery chain has issued an apology to roughly two million customers regarding a data breach that occurred earlier this year, during which hackers gained access to sensitive information such as names, addresses, phone numbers, birthdates, and purchase histories.
Loblaw, headquartered in Brampton, Ontario, runs approximately 2,500 locations across the country under its flagship Loblaws name, in addition to various sub-brands like No Frills, Real Canadian Superstore, Zehrs, and Fortinos.
In March, Loblaw revealed that unauthorized activity had taken place “in certain Loblaw technology systems” around February 23. An email sent this week to affected customers indicated that an internal investigation had determined that an “unauthorized third party” had accessed specific personal information.
“We understand that you trust us to safeguard your information, and we take that duty very seriously,” stated Loblaw CEO Per Bank in the email reviewed by CBC News. “We apologize for any distress this may cause and are dedicated to assisting you and ensuring the protection of your information.”
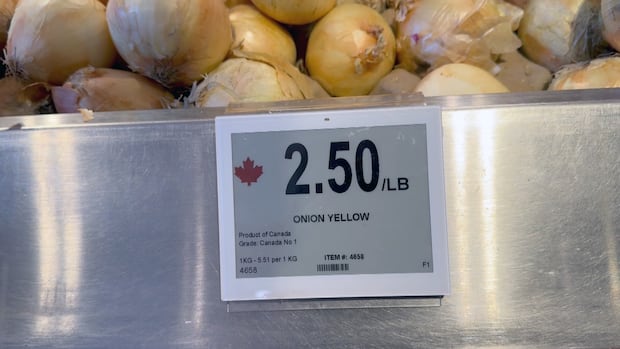
Just weeks after removing country-of-origin labels from the produce section of most provinces’ stores, Loblaw reversed the decision after being contacted by CBC News, and in the face of a renewed trade war with the U.S. and customer backlash.
As a safety measure, Loblaw reports that customers were logged out of applications utilizing the company’s PCiD credentials. This includes loyalty schemes like PC Optimum, the PC Express online grocery service, and the PC Financial portal.
The retailer is providing two years of complimentary credit monitoring and identity recovery services through TransUnion. Affected customers have until February 28, 2027, to register.
-
Save-On-Foods loyalty program members had personal information accessed in cybersecurity breach
-
CBC Investigates
Crime Stoppers had ‘potentially one of the most harmful data breaches’ Canada has seen. What’s next?
Loblaw is also cautioning recipients of the email to “remain vigilant” about unsolicited emails, calls, or texts requesting personal information or prompting them to click on links or download attachments.
“Monitor your accounts closely and notify the respective organization of any suspicious activity,” the CEO advises in the email.
Understanding credit monitoring services
Consumers should be aware that credit monitoring services provide limited protection, according to Cat Coode, a privacy and data strategist from Waterloo, Ontario.
“It primarily alerts you if someone tries to use your information to apply for credit or certain government documents. It doesn’t encompass the full range of possible uses for that data,” she explained to CBC News on Friday.
“The privacy issue can never be fully resolved … Once your data is out there, it’s out there. … You can change your credit card number, but you cannot change your birthdate.”
More than a ‘slap on the wrist’?
Every organization in Canada is legally required to safeguard the personal information they collect, states Maanit Zemel, a lawyer in Toronto specializing in internet, privacy, and cybersecurity law.
“It’s a regulatory requirement set forth by both federal and provincial privacy laws.”
At the federal level, the Personal Information Protection and Electronic Documents Act governs this issue. However, Zemel describes PIPEDA, which was enacted in 2001, as “stuck in the 90s.”
In June, the government put forward Bill C-36, the Protecting Privacy and Consumer Data Act, which seeks to significantly reform Canada’s privacy framework for the private sector, updating the terminology to recognize privacy as a “fundamental right” and replacing portions of PIPEDA.
Additionally, the bill mandates that companies perform a “privacy impact assessment” before transferring personal data outside of Canada.
If this legislation is approved, Zemel suggests that it will greatly enhance the repercussions for companies that mishandle customer personal data.
“It will no longer be just a slap on the wrist,” he remarked. “There will be significant penalties for failing to comply with these requirements, including implementing appropriate security measures.”
Tag: rewrite-pending